
About UK Cyber-Safe
We answer to the board, not to a vendor
UK Cyber-Safe is an independent cyber and AI governance practice working with UK organisations, based in Manchester. We do not sell software, we do not resell anybody else’s, and we take no commission from vendors. What we sell is judgement and the evidence that goes with it.
Why we exist
Most UK organisations under a few hundred people have no security function, and no realistic prospect of hiring one. The questions arrive anyway. A customer sends a security questionnaire. An insurer asks what has changed since last renewal. A director wants to know whether anybody checked the AI tool before it was switched on.
None of those are technical questions. They are governance questions, and the reason they go unanswered is rarely that nobody cares. It is that nobody owns them. There is an IT manager already fully occupied, a finance lead who signs things, and a board that has never been given the information it would need to decide anything.
AI has widened that gap faster than anything we have seen. Organisations are deploying it quickly, and the oversight is nowhere near it.
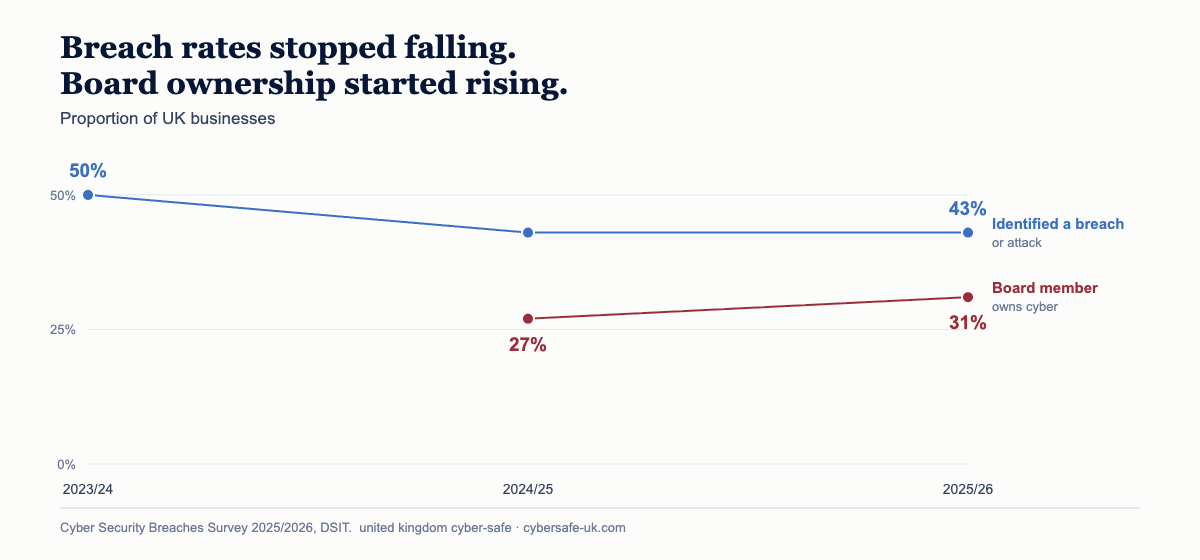
43%of UK businesses identified a cyber breach or attack in the last 12 months, which is about 612,000 businesses
31%have a board member with explicit responsibility for cyber security, up from 27% a year earlier. In large businesses it is 68%
1%reported ransomware, down from 3%. The rare event is not the one that decides your year
Cyber Security Breaches Survey 2025/2026, Department for Science, Innovation and Technology, published 30 April 2026.
How we work
Three rules we do not bend
We never assess our own work, and never sell the fix for what we assess.
An assessment is only worth something if the person doing it has no stake in the result. If we have designed your controls or written your policies, we will not then turn round, assess you and tell the world you passed. It costs us work. We think that is the point.
Our method is published before you engage us.
The thirty-six controls we assess against are on this site in full, with the evidence each one requires and what it maps to in UK law. You can read it, disagree with it, or work through it yourself without paying us anything.
The output is evidence, not a score.
A number out of ten helps nobody. What helps is a dated document you can hand to a customer, an insurer or the ICO that shows what you looked at, what you decided, and why.
So there is no confusion
What we are not
We are not an accredited certification body, and nothing we issue is a certification. Where a recognised mark is what you actually need, we will say so and help you get ready for it.
We are not a managed security provider. We do not monitor your systems or run your firewalls.
We are not a reseller. We hold no vendor partnerships and earn nothing on anything you buy.
We work with UK organisations only, under UK law. Client assessment records are held in the United Kingdom; our website is hosted in the United States, as our privacy notice explains.
The people who do the work
Three named leaders, and a bench of specialists
Gareth Morgan, Chief Executive Officer, signs the engagement and owns the price, the scope and the refusals. Ingrid Lindberg, Chief Information Security Officer, signs off every technical claim before it reaches a board. Alistair Donnelly, Chief Privacy Officer, owns the legal position where the security answer and the law differ. Behind them sit specialists engaged by discipline — testing, forensics, AI assurance, and the Crown Dependencies.
We publish qualifications you can check with the bodies that issue them. We do not publish employment histories, and the page explains why that is a deliberate decision rather than an omission.
Start with a conversation
Tell us what has been asked of you and who is asking. We will tell you what we think it needs, and whether that is us. There is no charge for the first conversation and no obligation at the end of it.